
Europe Cannot Regulate Stablecoin Demand Away, Says WeFi CEO
MiCA, the EU’s Markets in Crypto-Assets Regulation, has given crypto firms a single European rulebook and, with it, a bill. As the framework takes full effect, the loudest voices in the debate have been stablecoin issuers and exchanges.
WeFi sits elsewhere: it describes itself as an infrastructure-led on-chain finance company, and its chairman, Reeve Collins, co-founded Tether.
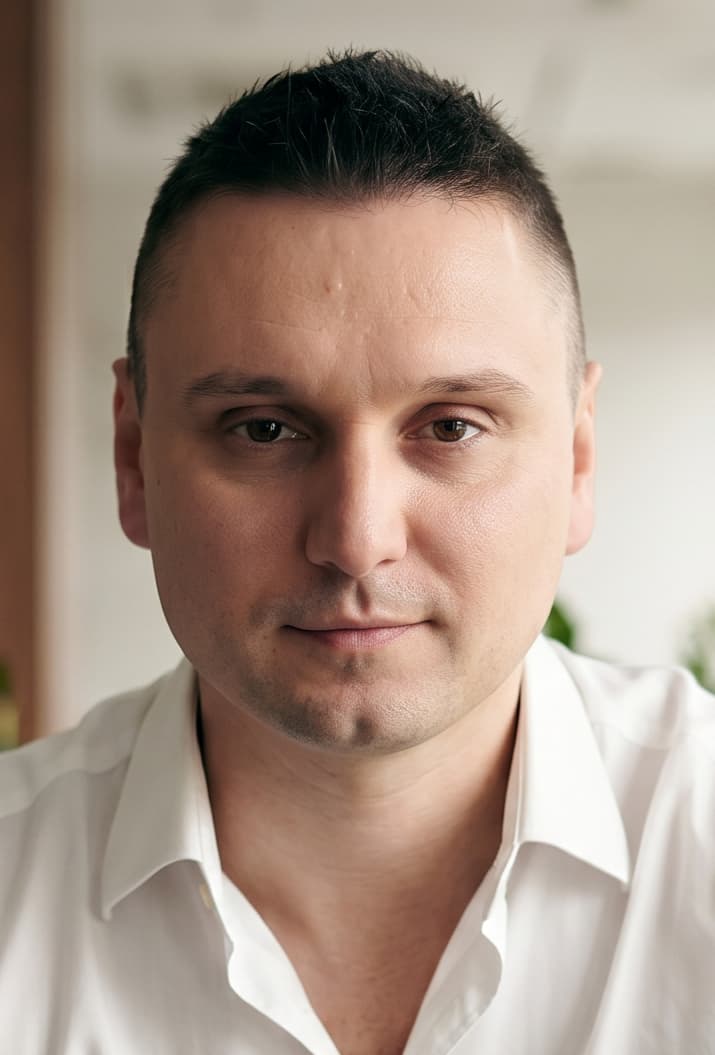
CEO and co-founder,
WeFi
Maksym Sakharov, CEO and co-founder of WeFi, answered The Fintech Times’ written questions on where an infrastructure company actually sits under the regime, what compliance really costs, and which parts of MiCA he would keep if he were writing the rules himself.
Where does WeFi actually sit under MiCA? The regime has largely deferred on genuinely decentralised finance, so are you commenting on rules that bind your centralised competitors more than they bind you?
WeFi should be understood first as an infrastructure-led company, not as a stablecoin issuer or a centralised exchange. That distinction is important, but it does not make MiCA irrelevant. MiCA is activity-based, so the question is not whether a company uses decentralised infrastructure. The question is which regulated activities are performed, who faces the user, who controls access, and which partners provide custody, transfer, exchange, or other crypto-asset services.
So the honest answer is that WeFi does not sit in the same place as a centralised exchange listing tokens for EU users, and it should not pretend that every part of the stack is untouched by MiCA either. The regulatory analysis has to follow each product flow and each access point.
That is the more interesting MiCA question for infrastructure companies. Regulation is no longer only about the asset or the protocol. It is about where infrastructure becomes a service, where a service becomes user-facing, and where responsibility sits in that chain.
Reeve Collins co-founded Tether and chairs WeFi. Tether’s position under MiCA has been the single most visible test of the whole regime. What is WeFi’s honest read on it?
WeFi cannot speak for Tether, and it should not turn this into issuer-specific commentary. The market lesson is clearer: MiCA showed that regulatory eligibility and user demand are now two different forces in the European stablecoin market.
USDT remains one of the most liquid and widely used dollar stablecoins globally, but MiCA changed access through regulated European platforms. Demand for dollar stablecoins did not disappear simply because platform availability changed. What changed was the compliant distribution route inside Europe.
This exposed a real gap in the market. Regulators want authorised, redeemable, supervised stablecoin products. Users and businesses want liquidity, acceptance, and dollar-denominated utility. The strongest stablecoin infrastructure in Europe will need both. If a regulated product does not match the liquidity and usefulness users already rely on, activity may move through less visible routes instead of becoming safer.
The lesson from the USDT situation is that Europe cannot regulate demand away. It has to build compliant channels that are useful enough to keep demand inside the regulated market.
‘How companies are adapting’ covers two very different things: genuinely complying, and simply geofencing European users out. Of the firms you deal with, roughly what proportion chose which?
I would not give a proportion without verified internal data, because that would create a false level of precision. But the split in behaviour is real. Some firms are building toward compliance: authorisation, legal restructuring, product changes, documentation, monitoring, partner reviews, and clearer user protections. Others have limited services, stopped onboarding EU users, or geofenced parts of their product because the cost or timing does not work for their current model.
The second category is important because it tells us something uncomfortable about MiCA. Regulation can improve market quality, but it can also reduce visible participation if the route to authorisation is too slow, expensive, or uncertain for smaller firms.
Geofencing is not always avoidance in a bad-faith sense. Sometimes it is a risk-control decision while a company works out whether Europe is commercially viable. But if too many serious builders choose exclusion over compliance, Europe gets a cleaner regulated market on paper but a smaller one with reduced innovation base in practice. Some activity is lost altogether, which reduces access, competition, and product development. Other activity may move to less visible and less compliant platforms, which weakens transparency and user protection. Neither outcome serves users well, and that is the part policymakers should watch closely.
MiCA’s stablecoin rules push issuance towards euro-denominated, e-money-style structures backed by European institutions. Is that consumer protection, or industrial policy for the euro wearing a consumer protection badge?
It is consumer protection with a strategic euro objective attached to it. The consumer protection case is straightforward: if a stablecoin is used for payments, users need reserve quality, redemption rights, issuer accountability, disclosures, and supervision. Those are not cosmetic requirements. They decide whether a payment instrument can hold confidence under pressure.
But Europe is also making a market-structure choice. It does not want the next layer of digital settlement to be dominated entirely by offshore dollar instruments, especially if those instruments become relevant to commerce, treasury flows, and consumer payments. That concern is about monetary sovereignty as much as consumer safety.
The risk is that Europe creates the right legal structure but not enough commercial utility. A euro-denominated, e-money-style stablecoin can satisfy regulators and still fail to attract users if liquidity, acceptance, pricing, and cross-border usefulness are weak. So the straight answer is yes, there is industrial policy inside the consumer protection framework. The test is whether that policy produces usable payment infrastructure, not just compliant issuance.
What has MiCA actually cost a firm of WeFi’s size, in money, headcount and time?
The better answer is to describe where the cost actually sits. MiCA is not just a legal bill. It affects product design, partner due diligence, jurisdictional analysis, compliance operations, documentation, monitoring, governance, and time to market.
For a company of WeFi’s type, the most expensive part is often not one application or one policy document. It is the repeated work of mapping what each product flow does, who touches the user, where custody or transfer activity may arise, which partner is responsible for which regulated function, and what controls need to exist before launch.
That cost repeats as soon as a company expands beyond one jurisdiction. Every new market brings another regulatory interpretation, another review process, and another set of operating requirements. When regimes diverge too sharply, expansion becomes a commercial calculation as much as a compliance exercise: is the opportunity large enough to justify another layer of legal work, product adjustment, partner validation, and operational controls? Greater alignment between jurisdictions, with room for local requirements where necessary, would make responsible cross-border infrastructure easier to scale.
That creates headcount pressure even when the company does not hire a large standalone compliance department. Product, legal, operations, finance, partnerships, and engineering all lose time to regulatory design. That is the real cost: fewer shortcuts, longer launch cycles, and more decisions that have to be made before a product reaches users.
What did MiCA get right? Which parts would you keep if you were writing the regime yourself?
MiCA got the need for a common European baseline right. Before MiCA, companies had to navigate a fragmented regulatory map across member states, which made serious product planning harder. A single framework for crypto-asset services, authorisation expectations, disclosures, custody, and user protection is directionally useful.
I would keep the principles around reserve transparency and redemption expectations for stablecoins. If a digital asset is used in payment or settlement activity, users need to understand what stands behind it, how redemption works, and who is accountable if confidence comes under pressure.
I would also keep the focus on market integrity. Clearer expectations around disclosure, conflicts of interest, and market abuse are necessary if crypto infrastructure is going to support broader financial activity.
Where MiCA still has to prove itself is implementation. A strong framework should raise standards without making the market accessible only to the largest incumbents. The best parts of MiCA are the parts that improve trust; the unresolved question is whether Europe can preserve competition while enforcing them.
If in two years the European crypto market has consolidated into a handful of licensed incumbents and the DeFi opening never arrives, what will you have been wrong about?
If that happens, the point to revisit would be whether MiCA’s common European baseline was workable enough for competition, not only strong enough for supervision. A single framework is better than fragmented national regimes, but clarity does not automatically make compliance affordable, reduce time to market, or give smaller companies a practical route to operate.
A market concentrated around a few licensed incumbents would show that Europe improved trust and oversight faster than it improved access for serious new entrants. That would not make MiCA irrelevant or unsuccessful. It would mean the framework raised the standard for participation without creating enough room for new infrastructure companies to build at speed.
The DeFi question would point to the same issue. If genuinely decentralised infrastructure never receives a practical regulatory opening, Europe may have clear rules for regulated interfaces while more protocol-level experimentation develops elsewhere.
The reassessment would be around implementation, not the need for regulation itself. A safer market still needs enough room for competition, experimentation, and new payment infrastructure to develop.